Monday, 7 October 2019

What do you get when you cross a Mouse with a Duck?

A Douse? A Muck? Sounds like the start of a bad joke doesn't it?

Well it's no joke. It's actually a sneaky way of attacking a computer system where the user doesn't even know what's going on and it give you an undetectable* way of getting access to all sorts of goodies.

Firstly the mouse. It's just a simple USB cabled mouse. There are thousands on the market and people use them day in, day out. Yes there are a lot of cordless mouses around these days. And keyboards. But I wanted something that could be dropped in a Corporate environment and people would use unwittingly. A simple Mouse it is then.

Next the Duck. Well anybody who does any sort of hardware hacking must have come across a Rubber Duck from that infamouse (sic) provider Hak5.
They're simple to use. Simple to install. And does the job very well. Albeit in a somewhat restricted and kind of expensive way.

But I'm a cheapskate and wanted a little more flexibility.

Enter the Raspberry Pi.

The RPi Zero-W has an extremely small footprint. It also offers on-board WiFi, a bi-directional USB port and a programming arena which is extremely familiar to me. Moreover somebody has already done half the work for me.

The next big problem is fitting the RPi inside the mouse. You can't just plug it in. It has to exist in the USB infrastructure. Which means that I need a USB hub inside there as well. This is easily done in the form of a USB Nano hub.
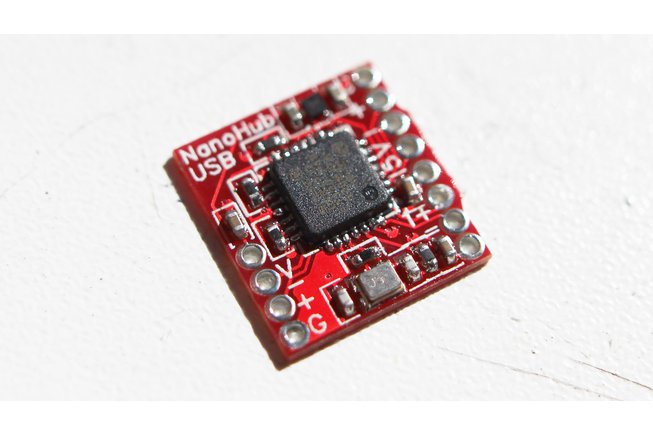
  
By de-soldering the USB wires that go to the mouse and attaching them to the input section (on the left in the image above) then soldering some spare wire from the top right port back to the mouse board we have a fully functioning mouse again.

The other port goes to the cut off section of a micro USB cable which in turn is plugged into the bi-directional port on the RPi. Plug in a micro SD card with the installation and you're good to go.

Obviously I added a few more options to the standard build to suit my needs. Firstly I went for a silent install for most options. No opening up Notepad and sending commands to say that everything is running. The idea is to be under the radar as much as possible.

So what can the RPi do? Well it identifies itself to the operating system as a device of your choice. I have it configured to boot into various modes emulating a wide variety of devices. It can tell the system that it is:

  • a mouse
  • a keyboard
  • a CD Drive
  • a DVD drive **
  • a USB Storage device (aka thumbdrive) **
  • a digital camera (PTP protocol) **
  • a network adaptor.

The on-board WiFi adaptor is how I connect to the device and tell it to perform whatever commands are necessary.

For purely visual purposes the default option is to configure itself as a keyboard. That way people are easily impressed when the computer suddenly starts typing things, or more often as not, suddenly starts playing a Youtube video in full screen mode. But behind the scenes there is so much more you can do with this device. For example when I start the system as a Network adaptor I basically lie to the OS telling it that it has a fantastic response speed (it doesn't) so that it will root all network traffic though it. Of course this then goes to my own computer, and through it out of another network interface back to the Internet. Meanwhile I'm sitting in the middle with Wireshark logging everything. Oh it's even more fun if it's in a Corporate environment where the default option is to install Corporate certificates to de-crypt and spy on all HTTPS traffic. Especially if you have the ability to re-encrypt using those self-same certs.

So why does this this technique work? Well basically because USB security does not exist. It is a fundamentally broken protocol. The only way around it is to block the ability to plug in USB devices.

But then again, who is going to suspect a simple mouse? Even if it is a Duck.


* Well yes, you can detect it... if you go looking at the hardware devices attached to your computer. But who goes looking for those except the extremely paranoid? Remember lsusb is your friend. USBGuard even more so.
** In digital storage mode, due to the limitations of the system it can only offer a maximum of 2Gb of data storage. More than enough to carry a decent payload or three. :)

Saturday, 11 August 2018

Fixing Kali vs Virtual Box Additions

Like most Pen Testers, I use Kali. However I'm running Kali under Virtual Box on Windows 7. Probably not the best option, but it's what I have to work with. But, and this is a big issue, Kali won't accept the Guest Additions which will allow me to cut and paste between Guest and Host, and map a shared drive. Not good when you need to gather evidence. So it's time to fix it.
Virtual Box 5.2.16
Kali 4.17.0-kali1-amd64
There are numerous articles out there on how to "fix" this issue. But the problem is, they don't work.

First problem is that apt-get update and such does nothing. I mean absolutely nothing. So lets check /etc/apt/sources.list
#
# deb cdrom:[Debian GNU/Linux 2018.2 _Kali-rolling_ - Official Snapshot amd64 LIVE/INSTALL Binary 20180412-10:55]/ kali-last-snapshot contrib main non-free
#deb cdrom:[Debian GNU/Linux 2018.2 _Kali-rolling_ - Official Snapshot amd64 LIVE/INSTALL Binary 20180412-10:55]/ kali-last-snapshot contrib main non-free
# This system was installed using small removable media
# (e.g. netinst, live or single CD). The matching "deb cdrom"
# entries were disabled at the end of the installation process.
# For information about how to configure apt package sources,
# see the sources.list(5) manual.
Do you see what's missing? Yep, no repos listed due to the way it was installed. I suspect this may be why many people are saying the "fixes" supplied don't work. Never mind, lets cat "deb http://http.kali.org/kali kali-rolling main non-free contrib"to the end of the file.

Now apt-get update and apt-get dist-upgrade work. Even if they do take a long time to upgrade properly.

So after waiting for all the updates to be done (a shade over 2 hours) now we need to get all the headers loaded to allow Virtual Box to build the additions. So the command to do this is:
apt-get install -y linux-headers-$(uname -r)
Right?

Wrong!

No, that's what you'd expect but that's not what you get. The name of the systems is different. They better option is to find out what headers you need.
apt-cache search linux-headers
This will dump out all the headers included with the build. Go to the top of the list and look for the "-all" option. Thats the one you want. So now, you can run:
apt-get install -y <whatever your build header is>
Finally after that is done (and after a reboot), you're ready to install the Guest Additions. Sort of. Running from the CDRom doesn't work, so remember to copy the file to your home drive.
root@kali:~#cp /media/cdrom/VBoxLinuxAdditions.run ~
root@kali:~# chmod 755 VBoxLinuxAdditions.run
root@kali:~/Desktop#./VBoxLinuxAdditions.run
And now you should be able to copy/paste to your heart's content.

Monday, 12 June 2017

Hacking TiddlyWiki (again)

So once again I'm back in Oxford hacking TiddlyWiki stuff.

Now I realise that I have seriously neglected this blog, because the last time I wrote about this was the last time I actually wrote an article. That's not because I'm not doing Tech Stuff, it's just that most of the Tech stuff I'm doing is not for public consumption.

So if you want to see an actually functional TiddlyWiki then try http://www.kizar.co.uk/TW/library.html

And somebody remind me to post here more often.

Saturday, 16 July 2016

Hacking TiddlyWiki

Now before you get all uppity, this is hacking in the traditional sense. i.e. making something better.

"But what on Earth is a TiddlyWiki?" I hear you ask.

Actually, it's kind of hard to describe. Well you've heard of Wikipedia? Imagine a personal version of Wikipedia that contains all your personal content of "whatever" in one easy to use system. Better yet, imagine a system where you don't actually need to use any software other than a web browser. To best describe it, in it's own words it is "a unique non-linear notebook for capturing, organising and sharing complex information."

At it's core each component of content is broken down into "Tiddlers". Essentially a text space with a title (and optional tags) which you can then cross link to other content. As such you can build up a complete web page for whatever kind of content you choose. But one of the best features of this system is that it is just an html file (with a lot of JavaScript that handles the core functionality. You can keep it on your personal file system, or because it is a web page, you can host on a web server, or better yet, via DropBox or other cloud services.

I am current at the TiddlyWiki European Meetup where we are working on the next versions of the core systems.

You can find your own personal TiddlyWiki at http;//tiddlywiki.com


Monday, 15 June 2015

Keeping your portable data "secure"

I recently attended the Info Security Europe conference held at Olympia, London. It was a huge three-day event (although I only went on the first day) with a number of high profile security, anti-virus and other related companies trade stands.

Not only that, but there were also a number of live hacking events, seminars, presentations of all-sorts (mostly sales pitches) and a few off-beat companies who provide specialist services.

I wasn't there for the sales pitches. Not interested in monitoring software. Not wanting to purchase hardware. I was looking for information and useful tools.

OK, I tell a lie. Although I wasn't looking to buy hardware, I did come across one company that was selling something a little unusual and very interesting. The company in question sold USB and SSD drives that were encrypted and hardware password protected.

The company in question was iStorage,

and the product which caught my eye was the datasur USB drive.

Now for years I've used a multi-boot USB drive for my most important tools. I used YUMI to handle the drive installation where I can boot the disk into multiple platforms. But this was on an unprotected drive, where if people could have got hold of it they could have used it as well. I had to use a TrueCrypt partition to protect some of the data on there, but it was always a pain loading the partition after the boot. So now there was the chance of having a secure drive right off the bat. So I bought one right there and then at the show.

A couple of days later and DHL dropped off a small packet with the enclosed drive. The device itself is very easy to use. It comes pre-formatted with a copy of the manual sitting in the root directory and a little data card which gives the default PIN and information about how to go about changing it. Needless to say, I changed the PIN. This was now my secure drive of choice.

So I fired up YUMI, got together a collection of my most useful .ISO images (which I always have handy anyway) and started getting things running. It was at that point my elation died as did, it seems, my drive. After running YUMI and installing my copy of Kaspersky Rescue Disk (always my first install of any new drive), the drive promptly detached and became unusable. Looking in the device manager it simply showed up as an unknown USB device. According to the instructions, if you get the access code wrongly ten times in a row then the drive should reset. So that's what I did. But to no joy, the device was still unusable.

So I contacted the iStorage support team to ask for help. They immediately dispatched a brand new drive without question. The failed disk I sent back to their Technical Support department. It was later determined that the failure was due to a faulty controller. Not due to an incompatibility with the YUMI multiboot configuration which was my first thought.

The moral of this story is one of user satisfaction. The iStorage Support Deptartment spared no expense to ensure that I, as a customer, was satisfied which their product. As in all businesses, if you don't have happy customers then your business model is wrong.


My only criticism with this device is an odd one. As I mentioned before if you enter the wrong code, 10 times in a row, then the drive is wiped and scrambled. So anybody who physically gets hold of your drive can blank it in just a few seconds and wipe all your valuable data. So there is a difference between accessible security and deletion security. It's harder to wipe a normal drive since you have to access it then wipe it via the computer.

But it all depends on what sort of data you keep on the drive. You did remember to keep secure backups of your important stuff didn't you?

Wednesday, 18 March 2015

Keeping Terry Pratchett alive

In Terry Pratchett's novel "Going Postal", anybody who dies in the service of the Clacks is kept alive by their name being transmitted over the wires. "A man is not dead while his name is still spoken," as one character puts it.

There has been a discussion on Reddit to immortalise Terry Pratchett's name in a similar manner. By adding his name to the X-Headers that are sent with every web request.

You can add this entry by simply selecting your website in the Web Configurations section of Domino and creating a Rule, like so:


My small contribution to a great man I once had the honour of meeting. I'll treasure my signed copy of the Colour of Magic.

Monday, 9 March 2015

DropBox and Server logs

If, like me, you run a few servers then your log files are vital to determining the health of your systems. The logs generated may be huge. Some are daily. Some are weekly. Some are only generated when a server encounters a problem and resets. Some are boring. Some are so damn useful in tracking down that annoying bug.

But all of them should be kept and analysed.

I've lost track of the number of times I've seen websites under attack. Some of these attacks are insidious in the way they are undertaken. The attacks themselves are spread out over time so that it's almost to distinguish the attacks from regular usage. Other attacks simply bombard your server with a high frequency that sends your server into fits of 404's and 500's.

But one thing you really need is to get those logs into a place where they can be assessed and archived. Now I have servers all over the place. But the servers which generate those logs are not accessible except via remote control which is time consuming and laborious to setup. So how can I get those logs into a central location?

Cue DropBox.

If you can install DropBox on the server then setting your log files to be dropped into a folder that is synchronised will allow those files to be sent to you whenever they change. It's simple and effective. But if you have many servers then this can become a bit of a pain. Having the same account might work for all your servers, but generally log files can grow to large sizes. DropBox can cope with this by simply ignoring the files that sent it over the limit. On your workstation you can then move the logs out into local storage clearing up space so that DB can then send down the remaining logs. DB is good like that.

But there is a better technique. One which can give you better overall control, but it does take a lot of organisation in the first place.

You will need an email address and account for all servers, plus a control (unless you wish to use your personal account). First register a control user which will act as your central "hub" for receiving your log files. Then send "invites" to all of the servers which you then wish to manage the logs of. Install DB on all of your servers using the invited emails. DB will give you a little bonus space for your servers, as well as a large bonus space for your control account. Once you have your accounts installed on your servers, you then need to create a shared folder for your log files. This is then shared with your control account.

Using this method gives you multiple benefits. Firstly, each server only has their own logs. you're not distributing the logs across all servers which is better for security. Secondly your control account now has an increased capacity for handling the logs. Always useful considering how many you will probably need to manage. Thirdly you have a better indication if any issues arise. A simple script can see which servers haven't yet communicated back their logs and you can then go and check out those servers for issues. That is unless you haven't been smart enough to set up other alerts for your systems in the first place.